Consequence-Based Risk Matrices for IEC 62443-3-2
Andrew Ginter shares a proposed IEC 62443-3-2 Appendix C: consequence-based risk matrices that replace likelihood with credibility for high-impact OT cyber attacks.
Andrew Ginter shares a proposed IEC 62443-3-2 Appendix C: consequence-based risk matrices that replace likelihood with credibility for high-impact OT cyber attacks.
Recommended guidelines on cyber security baseline requirements for Operational Technology (OT) systems were published in June 2026. I reviewed them…
OT security is “hard” – engineering change control (ECC) makes patching slow and expensive, many OT devices and systems have no real support for zero trust (ZT)…
Two decades ago, we founded Waterfall with one purpose: to defeat nation-state attacks impacting OT environments and critical infrastructure.
Anthropic’s Claude Mythos is the latest example of a trend many of us in industrial cybersecurity have been warning about for years.
If only we could wave a magic wand and patch everything and zero-trust everything, just like with our IT networks, then our OT networks would be “secure”
Ask different questions, get different answers. What should you be asking your OT “secure” remote access (SRA) vendor?
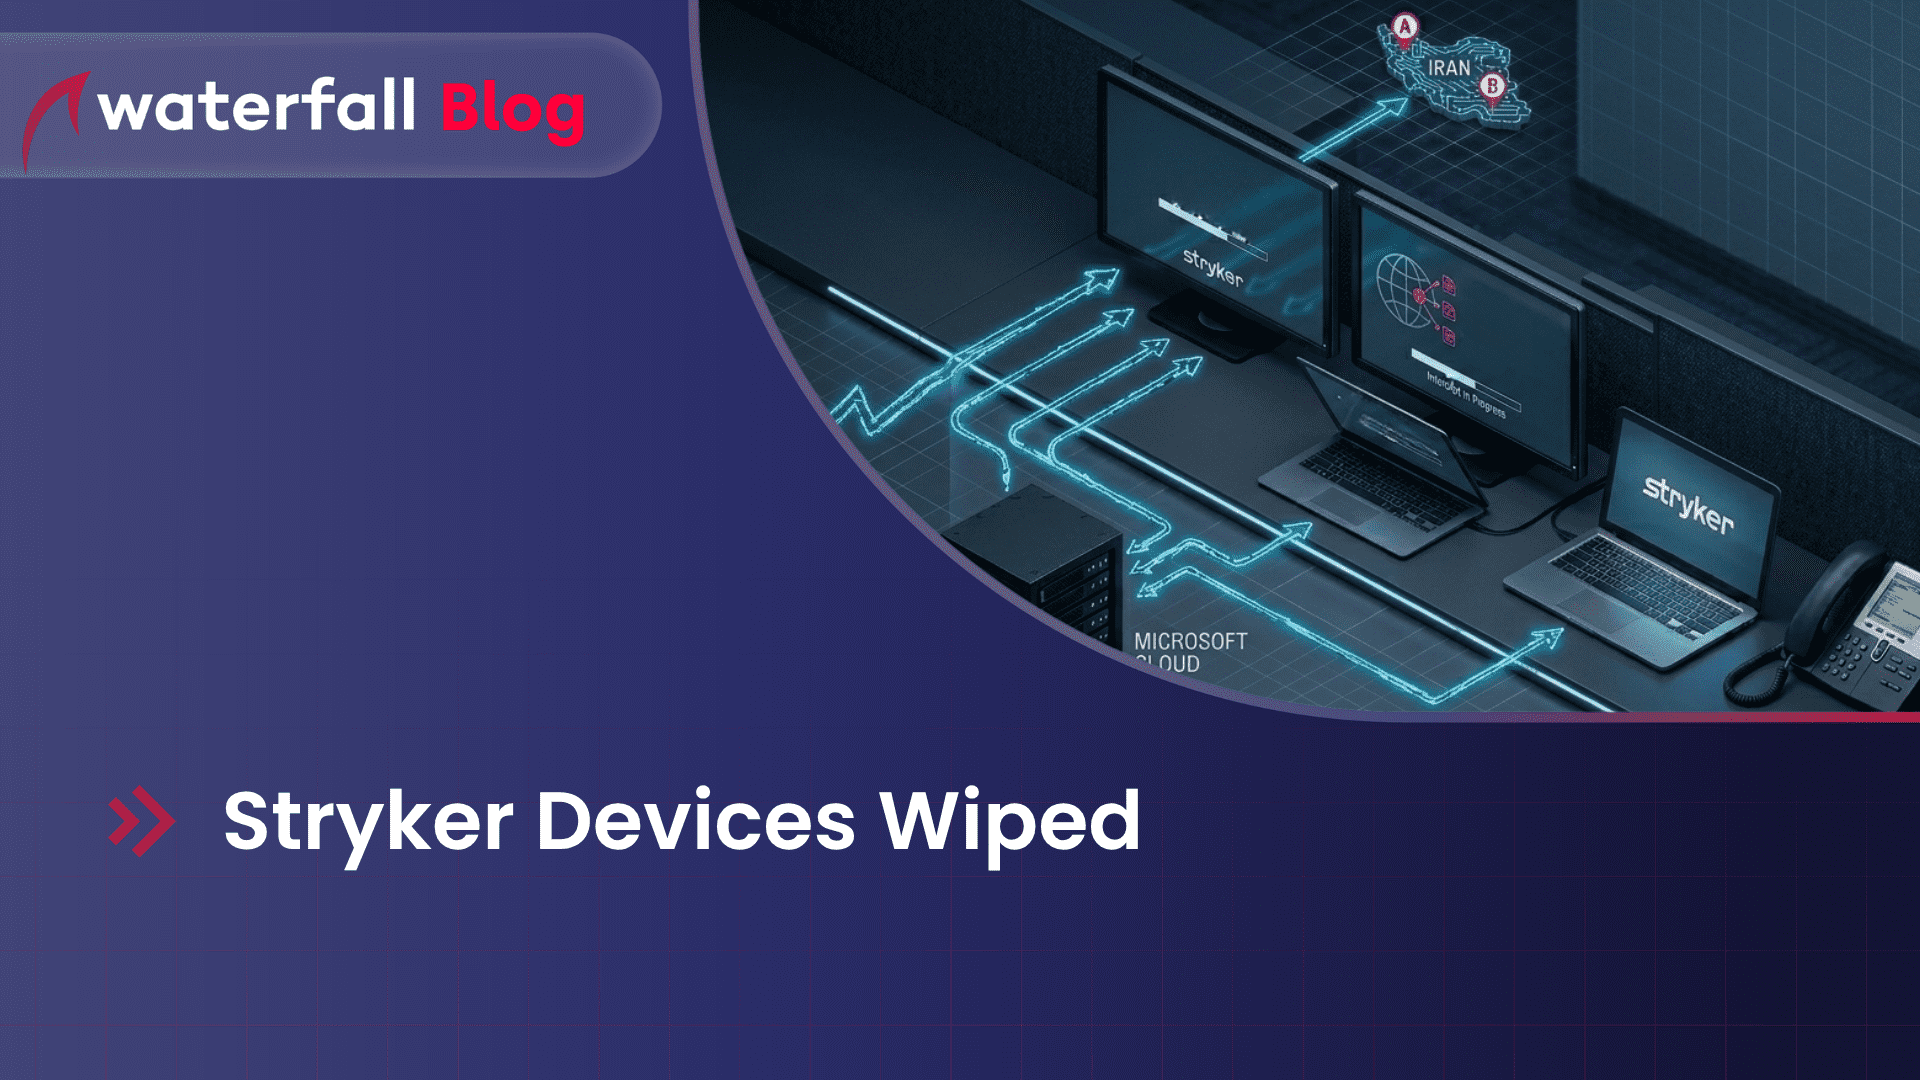
Stryker produces medical devices. An Iran-attributed attack erased 80K devices as a result of an intrusion into the Microsoft Cloud and an instruction to erase/reset the devices
The recognition of CIE highlights a broader shift in how cyber risk is being understood and managed in industrial environments
Waterfall Security is pleased to announce our inclusion in Gartner’s recent Market Guide for CPS Secure Remote Access report
